A familiar area code can create a false sense of trust. Criminals know that, and they are using caller ID manipulation to make fraudulent calls look local.
What happened
Internet-based calling technology makes it possible to disguise the true origin of a call. In a tactic often called neighbor spoofing, the number displayed on a phone may share the recipient’s area code or even resemble their own number.
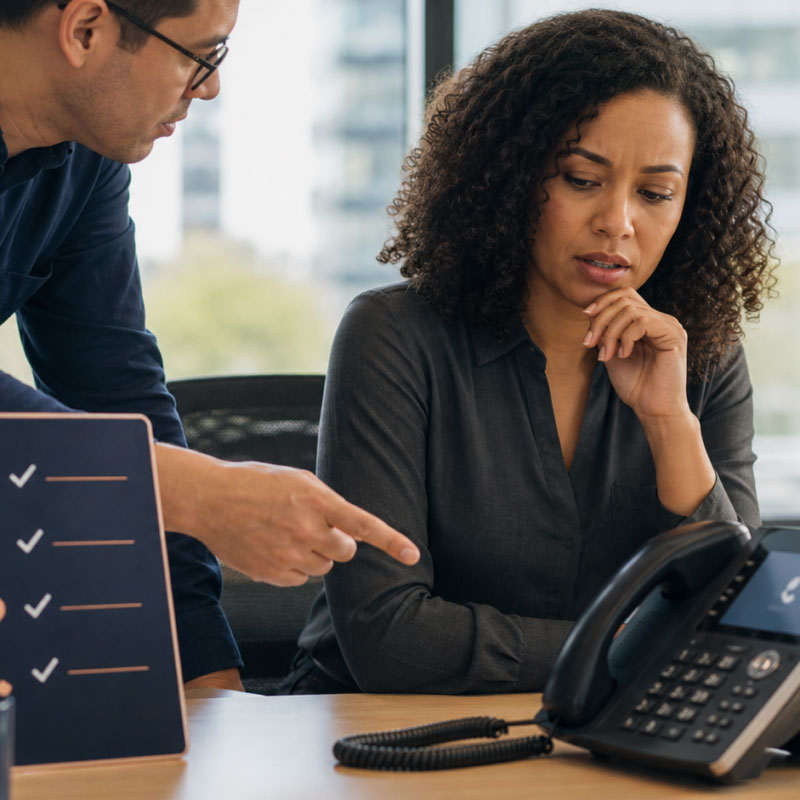
Once someone answers, the caller introduces urgency. The story may involve suspicious bank activity, a locked account, a delivery problem, a government demand, or a family member who supposedly needs help. The details change, but the objective is consistent: keep the person engaged long enough to obtain information, money, access, or another action.
Why this matters
This is more than a consumer nuisance. The same trust signals and pressure tactics can reach employees, finance teams, executives, customer-service staff, and help desks. A convincing call can become the first step in account compromise, fraudulent payment instructions, credential theft, or a broader social-engineering attack.
Answering can also confirm that a number is active, which may lead to additional attempts.
Who may be affected
Any organization whose employees receive outside calls should pay attention, especially when a caller asks for credentials, payment, account changes, confidential information, or an exception to an established process.
What to review now
- Let unfamiliar calls go to voicemail when there is no reason to expect the call.
- Do not rely on caller ID as proof of identity.
- Do not press buttons or follow instructions from an unexpected robocall.
- Verify banks, delivery services, government agencies, suppliers, and colleagues through an independently confirmed number or communication channel.
- Give employees a clear way to escalate suspicious calls without slowing down legitimate work.
Nadicent perspective
The strongest response is not simply another blocking tool. It is a verification process people can follow when pressure is high. Employees should know who owns the decision, how identity is confirmed, and where a suspicious request should go next.
Nadicent combines practical advisory experience with the specialist depth available through our Polaris back-office team and supplier portfolio. That broader bench helps organizations evaluate the people, process, and technology controls behind a security decision instead of treating each alert as an isolated product problem.
Not sure whether your current controls address social-engineering risk? Start a conversation with Nadicent.